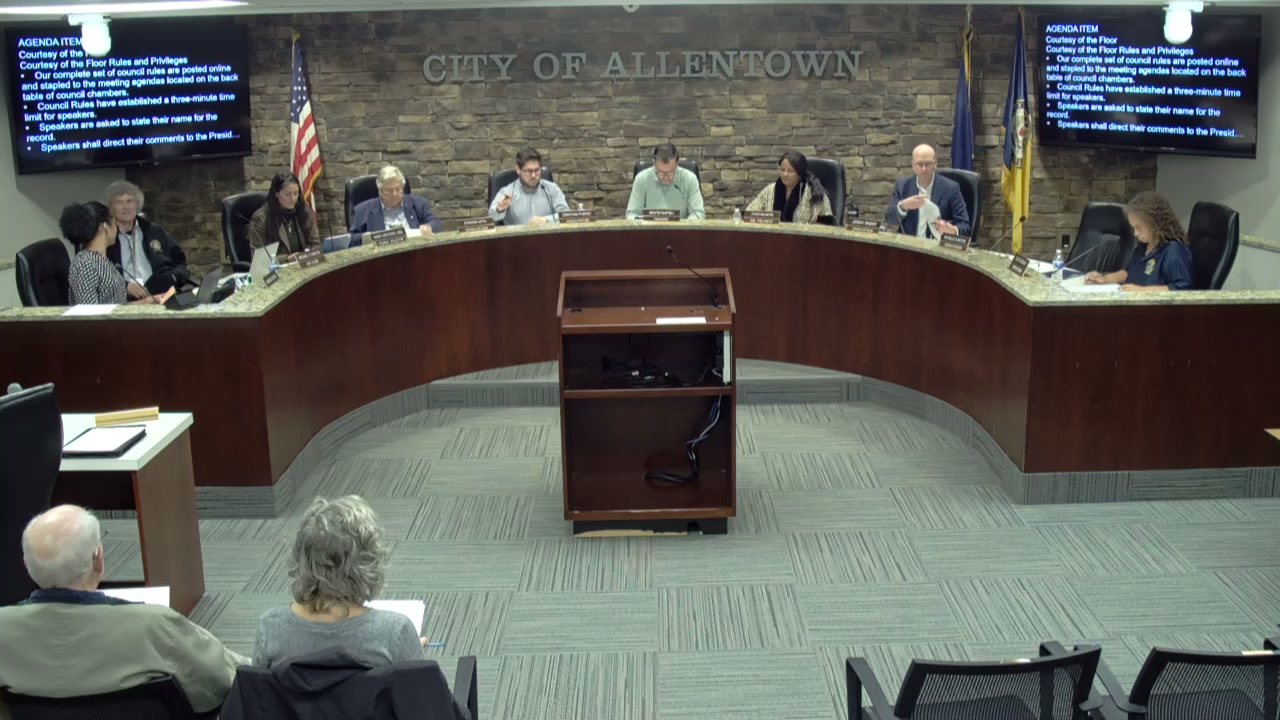
ALLENTOWN, Pa. — Allentown City Council’s livestream went down Wednesday after an outage at its video provider, Granicus, which took some products offline due to a critical flaw in PHP, software used to run websites.
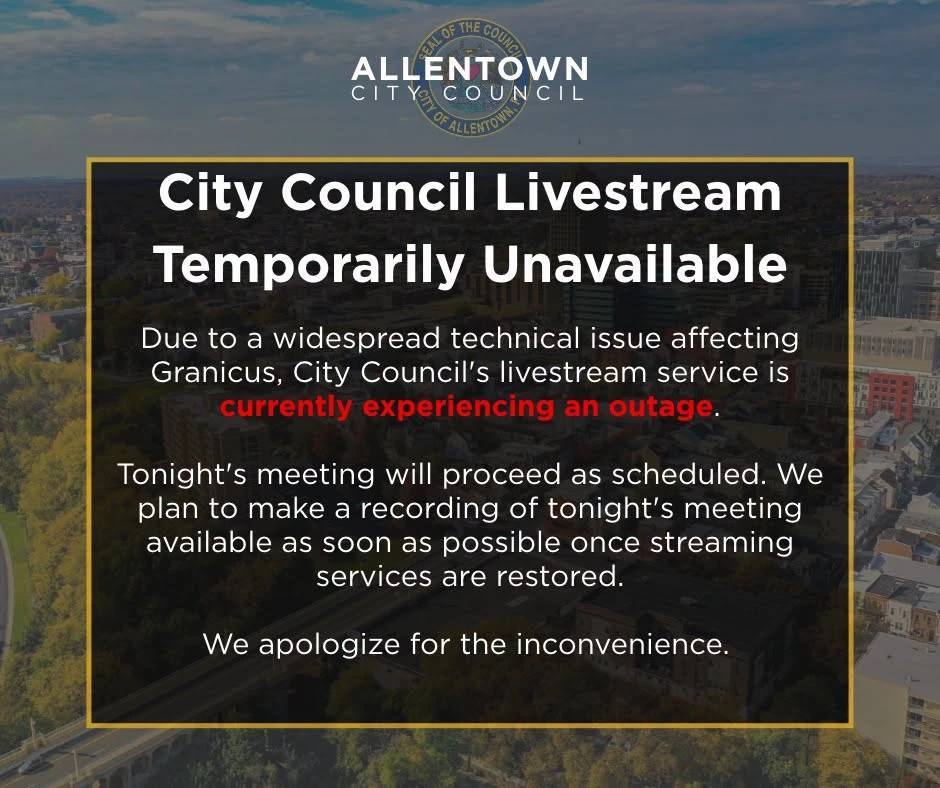
The city said in a notice that “a widespread technical issue affecting Granicus” caused the council’s livestream service to go offline. It said the meeting would go ahead as scheduled and that it planned to post a recording as soon as streaming returned.
Granicus said in a status update Wednesday: “We are aware of a recently identified PHP security vulnerability with widespread impact on internet services globally.” It later said its investigations were complete, that it knows of no breach of its systems and that it saw no sign of malicious activity.
By Thursday morning the video was back. Wednesday’s recording is posted on Swagit and runs 1 hour, 58 minutes. Swagit, a Granicus product, hosts the city’s council videos, according to the city’s meeting calendar. Granicus’s status page showed its video products working, with one product still being fixed: Legistar, the software behind the city’s calendar and agendas, which Granicus said is related to database connectivity.
PHP’s maintainers said in a security advisory that the two flaws, tracked as CVE-2026-109618 and CVE-2026-109619, can let an attacker run code on a PHP-powered web server without logging in. They released updates Wednesday at 10 a.m. Eastern, as announced a day earlier. The updates include versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35.
Governments elsewhere pulled websites offline over the same flaw before the updates were released, Reuters reported. It said agencies in the Netherlands and Finland took sites offline, and France’s Interior Ministry also took down local government administrative websites.
The Cybersecurity and Infrastructure Security Agency urged organizations in an alert Wednesday to update immediately. It said those that cannot, or that still use PHP 8.1 or earlier, should take their PHP systems offline until they are fixed. The agency said it had not seen the flaws exploited when it published the alert, though Cloudflare’s chief technology officer, Dane Knecht, said the web security company was seeing early attacks emerging, according to Reuters.
PHP’s advisory says versions 8.1 and older no longer receive updates from the project, though some vendors still provide fixes. The maintainers also published minimal patches for 7.4, 8.0 and 8.1 for people who build the software themselves.
WordPress security company Wordfence said Wednesday that updating WordPress does not fix the flaws and that site owners must update and restart PHP.
Council’s calendar lists the next meeting as a special budget session at 5:30 p.m. Oct. 28.